
Unified Identity Authentication & Admission
Unified identity authentication, strict secure admission
Unified identity authentication, strict secure admission
For government, state-owned enterprises and large offices — unified identity and business access
When user counts grow from dozens or hundreds to thousands and beyond, secure access is no longer only about “can they connect”.
- More people and more complex identities;
- More access environments — HQ, branches, remote work;
- Different roles need different business systems;
- Accounts, permissions and access records need unified management.
What you need is not just network access, but an identity-based secure admission model.
Confirm identity before permissions; define scope before reaching business systems.
One diagram: unified identity authentication and secure admission
TiSEC Unified Identity Authentication & Admission Platform
Large-scale identity authentication and secure access for government and enterprise, with unified identity management, strict access control and auditing, supporting MLPS compliance programs.
- Unified identity
- Large scale
- Strong authentication
- Permissions
- Security audit
- Compliance
Users & terminals
- Government staff
- Enterprise employees
- External personnel
- PC
- Mobile
- Dedicated terminals
- Other terminals


Identity authenticationTerminal admission
Identity management
- Account management
- Authentication
- Permission management
- Org structure
- Identity lifecycle
Secure admission
- Terminal identification
- Environment check
- Access control
- Policy management
- Dynamic admission
Audit & compliance
- Access logs
- Operation audit
- Behavior analytics
- Reports & statistics
- Compliance programs
- Unified authentication service
- Unified policy engine
- Unified operations management
Secure accessAccess control
Business systems
- Government apps
- Office systems
- Business systems
- Data center
- Other systems
Deployment options
- Government cloudFits government-cloud compliance and security requirements
- Private deploymentIndependent deployment, data under your control
- Hybrid cloudFlexible scaling, smooth transition
- On-premisesAdapts to specific environments and industry requirements


Core value
- Stronger securityOne identity, least privilege
- Higher efficiencyCentralized management, simpler operations
- Compliance supportSupports MLPS compliance programs; auditable and traceable
- Fits many scenariosFlexible deployment, stable operation


From “users can connect” to “identities are managed”
Traditional network access focuses on:
Can this user enter the network?
In government and enterprise offices, you also need to answer:
- Who is this person?
- Which terminal are they using?
- Which business systems can they reach?
- Do they meet current access requirements?
- Is the whole access process recorded?
TiSEC Unified Identity Authentication & Admission Platform ties users, terminals, permissions and business access together around identity authentication, delivering unified secure admission for government and enterprise offices.
Core capabilities
Unified identity
Bring different users into one identity management system — unified authentication and administration, with less complexity from multiple account silos.
- Unified identity
- Unified authentication
- Centralized management
Strict authentication
Authenticate users according to your security requirements, with mechanisms that match how strictly you need to verify identity.
“Who are you?”
Permission management
Different roles deserve different business scope. Set access by user, organization and real business needs so people reach only what their work requires.
- Need-based authorization
- Permission management
- Access scope control
Secure admission
After authentication, enforce your security policies before business access — connecting identity verification to reaching applications, not just joining a network.
- Identity → Permission → Business access
Access audit
Record authentication and access for security operations and investigation.
Who accessed, when, and what they reached.
- Authentication records
- Access records
- Security audit
Behind the solution, a working product
Unified identity authentication & admission brings authentication, admission and audit into one platform, with a mobile token app.
Confirm who you are, then allow access
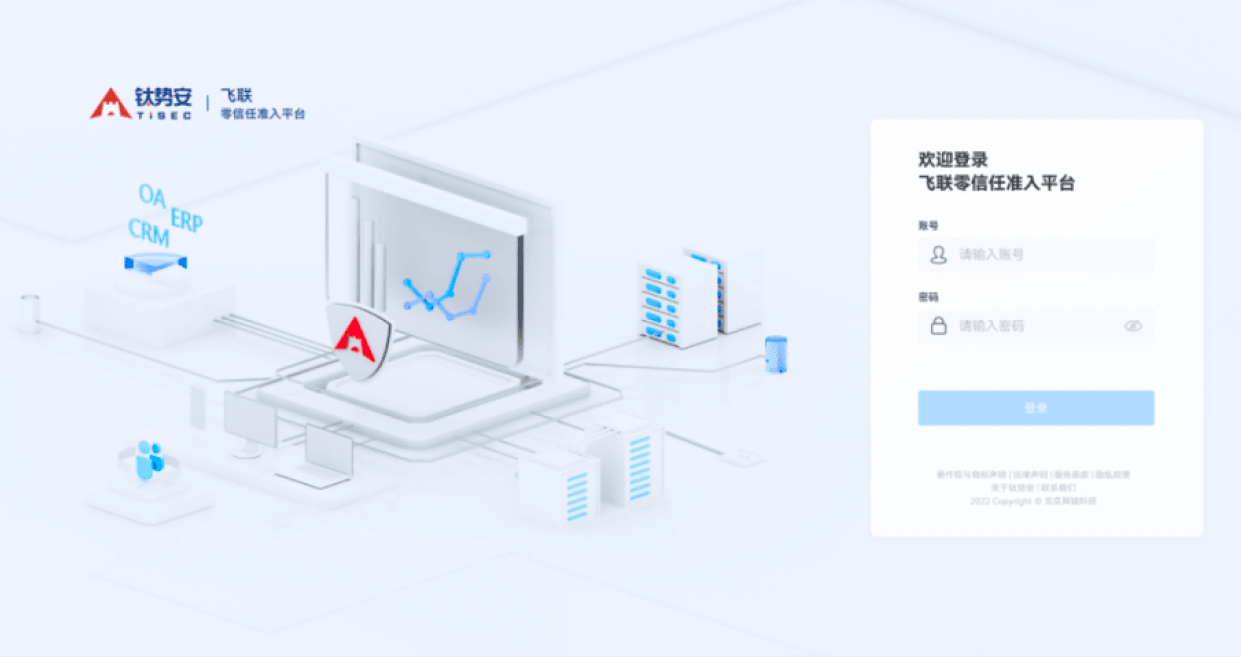
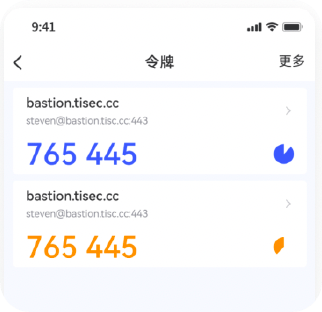
Users authenticate at a unified sign-in portal; where requirements are higher, a one-time passcode from the phone app adds another confirmation before business access.
- Unified sign-in
- One-time passcode
- Authenticate, then admit
Access at a glance for administrators
Users, endpoints, applications and access events in one view, together with authentication and access records for daily management and tracing.
- Centralized management
- Access records
- Security audit
Screens are product screenshots for illustration, dashboard figures are blurred; features and visuals follow the delivered release.
Why government and enterprise need unified identity
At scale, you cannot rely on “knowing everyone by heart”
In large government and enterprise environments, people come from many departments, organizations and locations.
When every business system manages its own accounts, you often get:
This platform addresses that layer of the problem:
Bring scattered access subjects into one identity management framework.
Move from managing many system accounts to managing user identities and access permissions.
From identity to business: the full access chain
- UsersStaff · Managers · Business users · Other authorized users
- Identity authenticationConfirm the access subject
- Secure admissionPolicy-based access decision
- Permission controlDefine allowed business scope
- Business systemsOA · ERP · Finance · Apps · Data resources
- Security auditRecord authentication and access
Deployment for different government and enterprise environments
The platform adapts to your existing infrastructure and build model.
Government cloud
Deploy in government cloud environments with unified identity authentication and secure admission for cloud business access.
Private deployment
Run in your data center or private cloud with full control of deployment and operations.
Hybrid environments
When some workloads are cloud and some on-premises, design deployment around your actual network architecture.
Cloud compatibility, domestic stack adaptation and deployment architecture depend on project environment and technical validation.
Typical scenarios
Government offices
Complex org relationships require unified identity and secure admission.
State-owned enterprises
Groups, subsidiaries and many org units with heavy user and business access needs.
Large enterprise offices
Many departments, users and systems — need one identity and permission model.
Multi-site work
HQ, branches and remote staff all need controlled access to internal business.
How is this different from SecureLink?
SecureLink
Solve: fast access to core business
For SMEs and private enterprises — lightweight, fast, foundational capabilities.
- Quick install
- Basic authentication
- Permission control
- Core business access
Unified identity admission
Solve: unified identity and secure admission at scale
For government, state-owned enterprises and large offices — large user bases, unified identity, strict authentication, permissions and audit.
- Unified identity
- Large user base
- Strict authentication
- Permission management
- Security audit
Unified secure admission in a zero-trust mindset
Built on zero trust — the goal is not “being on the intranet”, but:
- Who is accessing
- Are they trusted
- What can they reach
- Control and audit
Shift from traditional network access to business access centered on identity and permissions.
Let identity be the starting point of secure access
- People have identity
- Access has permissions
- Admission has control
- Actions leave records
- Unified identity
- Strict authentication
- Permission management
- Secure admission
- Access audit
Every business access by government and enterprise users rests on clear identity and permission.